
TL;DR
POS security is the combination of technologies and practices, like encryption, tokenization, and access controls, that protect a point-of-sale system from data theft, fraud, and unauthorized access.
POS security is the combination of technologies, policies, and practices used to protect your point-of-sale system, including its hardware, software, and network, from unauthorized access, data breaches, and fraud. It covers everything from how card data is encrypted at checkout to who has access to your back office and how quickly you can detect and respond to suspicious activity.
Every time a customer taps, dips, or swipes a card at your register, sensitive payment data moves through this system. If it isn’t secured properly, it becomes an open door for hackers, fraud, and data theft, putting your business, your customers, and your reputation at risk.
For independent retailers such as liquor stores, grocery stores, convenience stores, and smoke shops, this is not optional. These businesses handle high transaction volumes, cash and card payments, age-restricted sales, and often lottery transactions, all of which make them attractive targets for external hackers and internal theft alike. This guide breaks down exactly what POS security means, the threats you’re up against, and the specific steps you can take to protect your store.
What Is POS Security, and Why Does It Matter for Independent Retailers?
POS security protects three things at once: the data flowing through your system, the devices processing that data, and the people who have access to it. A point-of-sale system is not just a cash register; it is a network of connected devices, software, and payment processors, including the terminal, card reader, backend software, network, storage, and staff logins. A weakness in any single part can expose the entire system.
Your POS system stores customer payment information, employee credentials, inventory data, and daily transaction records all in one place, so a single vulnerability can expose all of it at once. For a small or independent retailer, the stakes are especially high:
- Financial loss from fraud, chargebacks, or stolen funds
- Legal and compliance penalties for failing to meet PCI DSS requirements
- Reputational damage that drives customers to competitors
- Operational disruption if systems go down during an attack or investigation
- Loss of customer trust, which is often harder to rebuild than the financial damage itself
Unlike large chains with dedicated IT security teams, independent stores often run lean, which makes choosing a POS system with strong built-in security even more important. Attackers know this, and small retailers are frequently targeted specifically because they are assumed to have weaker defenses than large enterprises.
Looking for a Secure POS System for Your Retail Business? Explore industry-specific POS solutions designed to keep your transactions and daily operations secure and efficient.
How POS Security Works: The Core Components
POS security works by layering multiple protections on top of each other, so if one layer fails, others are still in place to limit the damage. This “defense in depth” approach is what stops a single stolen password or vulnerable device from turning into a full data breach.
- Encryption (P2PE): Accurate. Point-to-point encryption ensures the POS software itself never handles raw credit card data, making memory-scraping malware ineffective.
- Tokenization: Accurate. Replacing actual card numbers with mathematically unrelated tokens prevents databases from becoming lucrative targets for hackers.
- PCI DSS Compliance: Accurate. This is the global baseline security standard governed by major credit card companies (Visa, Mastercard, etc.) that requires all the technical controls you listed.
- Multi-Factor Authentication (MFA): Accurate. MFA is a strict requirement for remote access to POS environments to neutralize stolen passwords.
- Network Segmentation: Accurate. Keeping the POS environment isolated prevents a breach on a less secure network (like a public guest Wi-Fi or back-office computer) from crossing over to the payment terminals.
- Role-Based Access Control: Accurate. Limiting privileges based on job function (the “principle of least privilege”) is a core tenet of access control.
- Real-Time Monitoring and Alerts: Accurate. Security Information and Event Management (SIEM) systems and intrusion detection are critical for catching anomalies as they happen.
- Application Allowlisting and Antivirus: Accurate. POS systems are highly restricted endpoints; locking down the system so it can only run the specific POS application prevents rogue malware executables from running.
- Audit Trails: Accurate. Logging all activity ensures that if an incident occurs, investigators can determine exactly how it happened, which is a specific PCI DSS requirement.
No single layer is enough on its own, but together, these components make it significantly harder for an attack to succeed or go unnoticed.
Common POS Security Threats Retailers Face Today
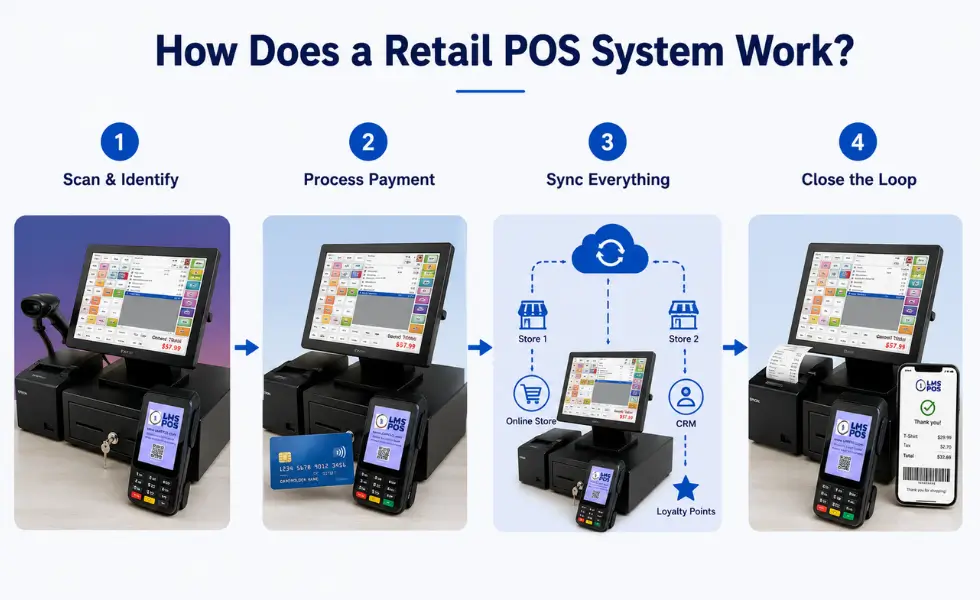
Every retail POS system faces a mix of digital, physical, and human threats, often working together rather than alone. Here’s what to watch for.
- POS malware. Malicious software that scrapes payment card data directly from a terminal’s memory during a transaction, often before the data is even encrypted. This has been behind some of the largest retail data breaches in history.
- POS skimming. Physical or digital devices attached to card readers that capture card details without the customer or retailer noticing. Skimmers can be installed in seconds and are built to blend in with the terminal.
- Insider fraud. Employees misusing register or back-office access to steal cash, manipulate transactions, void sales improperly, or exfiltrate customer data. This is often harder to detect since the activity looks like normal system use.
- Unsecured networks. POS systems sharing a network with guest Wi-Fi or unrelated devices give attackers an easier path in and let them move laterally toward the POS environment once inside.
- Weak or shared credentials. Generic logins, unchanged default passwords, or shared PINs make unauthorized access easier and make it nearly impossible to trace suspicious activity to a specific person.
- Outdated software. Unpatched POS systems leave known vulnerabilities open for attackers to exploit, sometimes for months or years after a fix is released.
- Physical tampering. Direct physical access to a terminal, whether from a dishonest employee or someone posing as a technician, can be used to install skimming hardware or extract data directly.
None of these threats work in isolation. Most breaches involve more than one weakness being exploited at once, which is exactly why layered defenses matter just as much as recognizing the risk itself.
Want to experience these benefits in your own store? Contact LMS POS to see how it automates inventory, speeds up checkout, and keeps every sales channel connected.
How a POS Breach Actually Happens
Most POS breaches follow a similar pattern, regardless of the specific malware or method used. Understanding these stages helps explain why layered security matters so much.
- Infiltration. An attacker gains initial access, often through a phishing email, a stolen credential, or an unpatched vulnerability in the network.
- Propagation. Once inside, malware spreads across connected systems until it reaches the POS terminals themselves.
- Exfiltration. The malware scrapes payment card data directly from the terminal’s memory, sometimes before encryption even applies.
- Aggregation. Stolen data is collected in one place within the compromised environment, then quietly moved out to a location the attacker controls.
Real-World Examples of POS Security Failures
POS breaches are not a theoretical risk. Some of the largest data breaches in retail history started with a compromised point-of-sale system.
- Target (2013): Attackers gained access through a third-party HVAC vendor’s credentials and installed memory-scraping malware on Target’s POS systems. It compromised the personal information of 70 million customers (along with 40 million payment cards) and resulted in a $10 million consumer settlement in 2015, alongside much larger payouts to credit card networks and banks.
- Home Depot (2014): Hackers used stolen vendor credentials to deploy malware across Home Depot’s self-checkout POS systems, exposing the payment card information of approximately 40 million customers, according to the DC Attorney General’s office. The company paid 13 million dollars into a consumer class action settlement fund, in addition to a separate 17.5 million dollar settlement with 46 state attorneys general.
- Wendy’s (2016): Malware was installed remotely on the POS systems of 1,025 franchised locations, leading to widespread credit card theft and massive class-action lawsuits from financial institutions, which Wendy’s eventually settled for $50 million.
These cases involved large retailers, but the same attack methods target independent businesses too, often specifically because smaller retailers are assumed to have weaker defenses and less monitoring in place.
What to Do If Your POS System Is Breached
A POS security breach can escalate fast, but the right response in the first few hours can limit how much damage it causes.
- Disconnect affected devices from the network immediately to stop the spread.
- Contact your payment processor so they can flag affected card data and monitor for fraud.
- Preserve logs and evidence rather than wiping systems right away, since this data is needed to investigate how the breach happened.
- Follow your legal notification requirements, since many states require you to inform affected customers within a set timeframe.
- Notify your POS provider so they can help identify the source and patch the vulnerability. Our technical support team is available 24/7 for exactly this.
- Review and tighten access controls before bringing systems back online, so the same vulnerability cannot be used again.
Responding well after a breach matters, but the better goal is preventing one in the first place, which comes down to the right defenses built into your POS system from the start.
POS Security by Business Type
The fundamentals of POS security stay the same everywhere, but the priorities shift depending on what kind of store you’re running.
- Liquor stores deal with high-value inventory, age verification requirements, and often lottery transactions, all of which need to be reconciled and audited daily to catch discrepancies early.
- Grocery stores process high transaction volumes and often accept EBT payments, which adds another layer of compliance and data handling to manage securely.
- Convenience stores combine high-volume checkout with lottery sales and age-restricted products, making fast, accurate audit trails essential.
- Smoke and vape shops face strict age verification and compliance requirements, along with high SKU counts that make inventory and transaction tracking more complex.
Across all of these, the fundamentals stay the same: encrypt data, restrict access, monitor activity, and keep a clear audit trail.
POS Security Best Practices Checklist
Strong POS security isn’t just about the right technology; it’s also about the daily habits that keep it working.
- Choose a POS provider that supports end-to-end encryption and is PCI DSS compliant
- Set unique, role-based logins for every employee and never share credentials
- Keep POS software and firmware updated with the latest security patches
- Physically inspect card readers regularly for skimming devices
- Monitor transactions in real time for unusual patterns
- Integrate security camera footage with transaction data to investigate discrepancies quickly
- Train staff to recognize phishing attempts and social engineering tactics
- Restrict system access immediately when an employee leaves
- Review user permissions periodically to remove unnecessary access
None of these steps require a large budget or a dedicated IT team; they just require consistency. A POS system is only as secure as the habits behind it.
How LMS POS Supports Point-of-Sale Security
Beyond the fundamentals, the POS system you choose plays a direct role in how secure your store actually is day to day. LMS POS is built for liquor stores, grocery stores, convenience stores, and smoke shops with security built into the everyday workflow, not bolted on as an afterthought.
- EMV payment processing with secure card handling at checkout
- NVR camera integration that syncs directly with your point of sale, so you can monitor transactions in real time and investigate discrepancies fast
- Built-in age and ID verification, helping protect your license and keep you compliant with state alcohol and tobacco laws
- Automated daily lottery reconciliation with instant alerts the moment ticket or settlement figures don’t add up
- Real-time sales dashboards and reports you can check from anywhere, not just the register
- 24/7 live technical support from real staff, so system issues do not sit unresolved
For independent retailers who cannot run a full-time IT security team, this kind of built-in protection matters as much as any single feature on the register.
Final Thoughts
POS security is not a single feature. It is an ongoing combination of the right technology, the right processes, and the right POS partner. From encryption and monitoring to understanding how breaches actually unfold, every layer plays a role, and no single safeguard is ever enough on its own.
For independent retailers handling cash, card, lottery, and age-restricted sales every day, the stakes are high, since a single breach can mean financial loss, compliance penalties, and lasting damage to customer trust. Choosing a POS system with security built into its foundation, backed by consistent daily habits, is one of the most effective ways to protect your business long term.
Not sure if your current POS setup is secure enough? Contact our team, and we’ll walk you through what’s working, what’s missing, and what to fix first.
Frequently Asked Questions
What is POS security?
POS security refers to the technologies and practices used to protect point-of-sale systems, including hardware, software, and networks, from data theft, fraud, and unauthorized access. It keeps every transaction and every device in the chain protected.
Why is POS security important?
It protects customer payment data, keeps your business compliant with PCI DSS, and prevents the financial and reputational damage caused by data breaches or fraud. A single breach can cost far more than prevention ever would.
How does POS security work?
It works through layered protections such as encryption, tokenization, network segmentation, access controls, and real-time monitoring. Together, these layers make it difficult for attackers to intercept or misuse payment data.
What are the best ways to protect POS data?
Use encryption and tokenization, enable multi-factor authentication, segment your network, apply role-based access control, and keep your POS software updated. Consistency matters as much as the tools themselves.
What is a POS security checklist?
A POS security checklist is a set of practical steps, such as enabling MFA, segmenting networks, restricting access, and monitoring transactions, that retailers follow to reduce their risk of a breach.
Do small or independent retailers really need advanced POS security?
Yes. Independent stores are often targeted precisely because they are assumed to have weaker security than large chains, which makes strong POS protections just as critical.
What should I do if my POS system is breached?
Disconnect the affected devices, contact your payment processor immediately, and preserve system logs for investigation. Then follow your state’s notification requirements and notify your POS provider to help patch the source.
Dipesh Shrestha
Dipesh Shrestha is the Co-founder of Compro Boston, maker of LMS-POS. With over two decades of hands-on experience in point-of-sale deployment, payment processing ecosystems, and retail hardware logistics, he specializes in building secure, highly optimized checkout environments.
